Who we are
EverCore is operated by MECHANICX LLC, a limited liability company registered in Wyoming, United States. In this policy, “we”, “us”, and “our” mean MECHANICX LLC, “you” means the Shopify merchant who installs EverCore on their store, and “buyers” means the people who shop on your store.
If you have a question about this policy or about the data EverCore handles, contact us at support@evercore.dev.
What EverCore does
EverCore is a Shopify app installed by a merchant onto their own store. It provides:
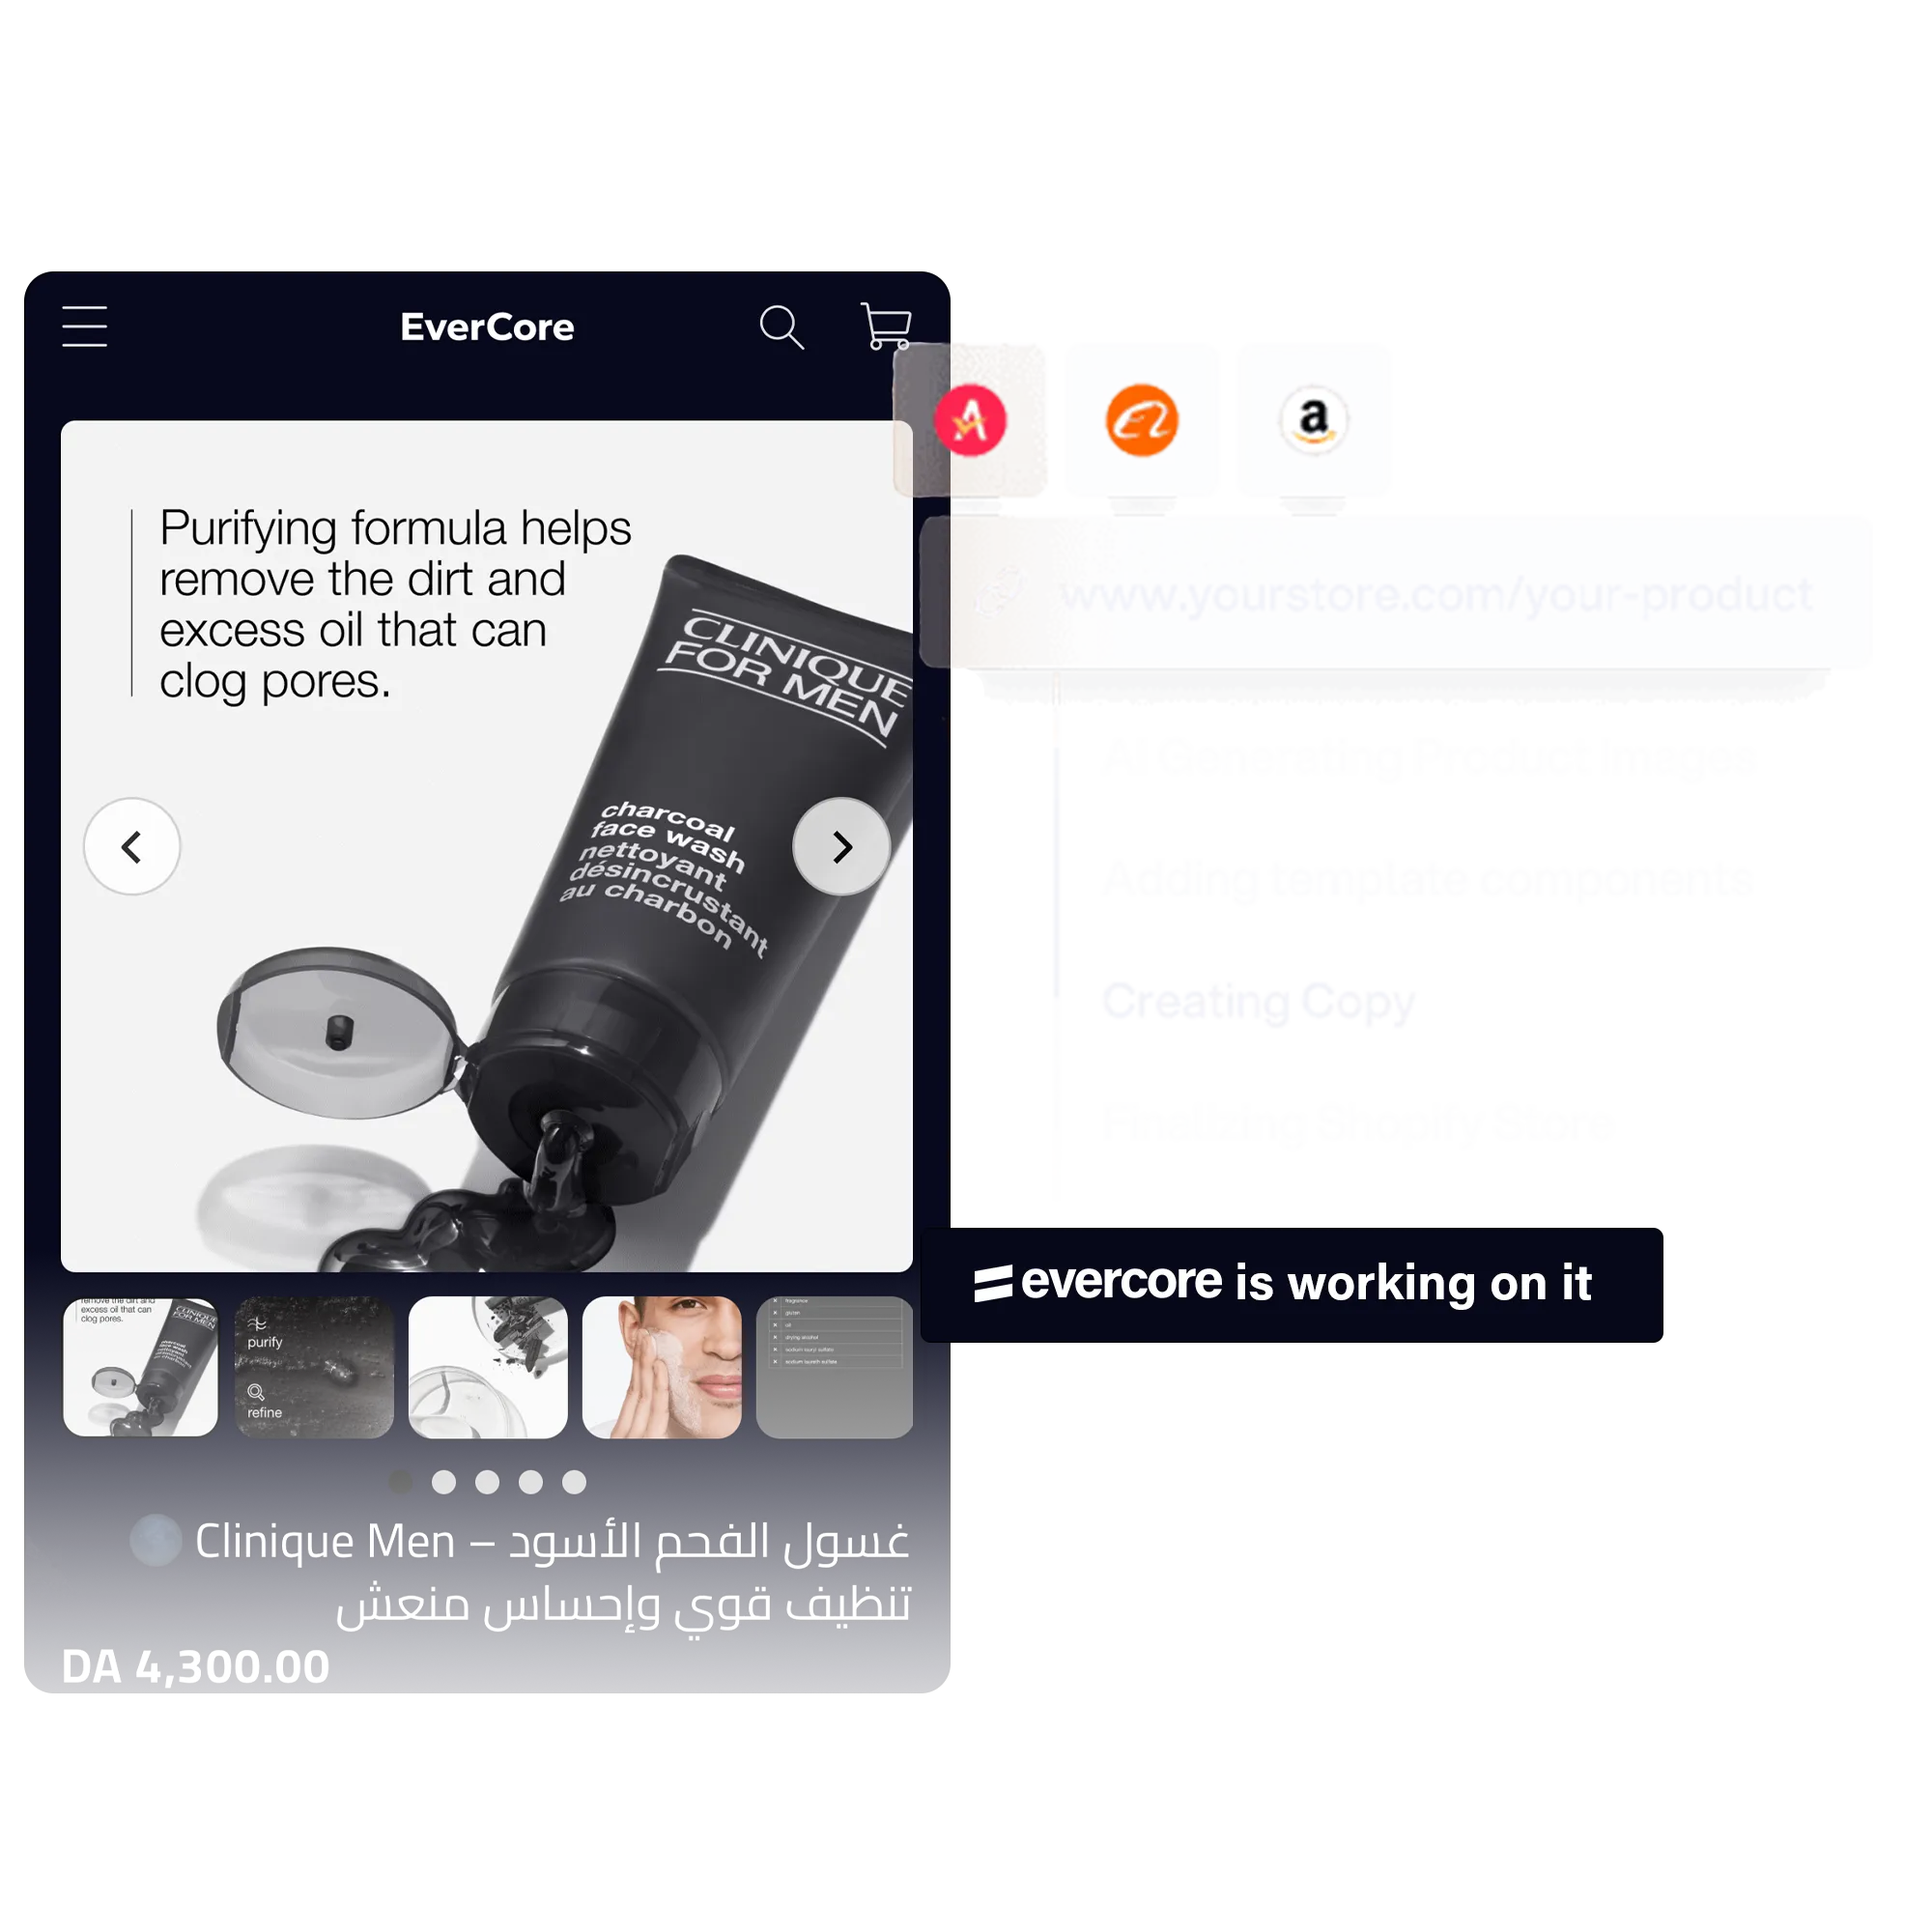
- Stores and product pages: import a product from your catalogue or from an AliExpress link, and generate a store or product page, with AI-written copy, inside a theme you choose.
- Landing pages: generate a landing page for a product, with AI-written copy and AI-generated images, in one of ten languages.
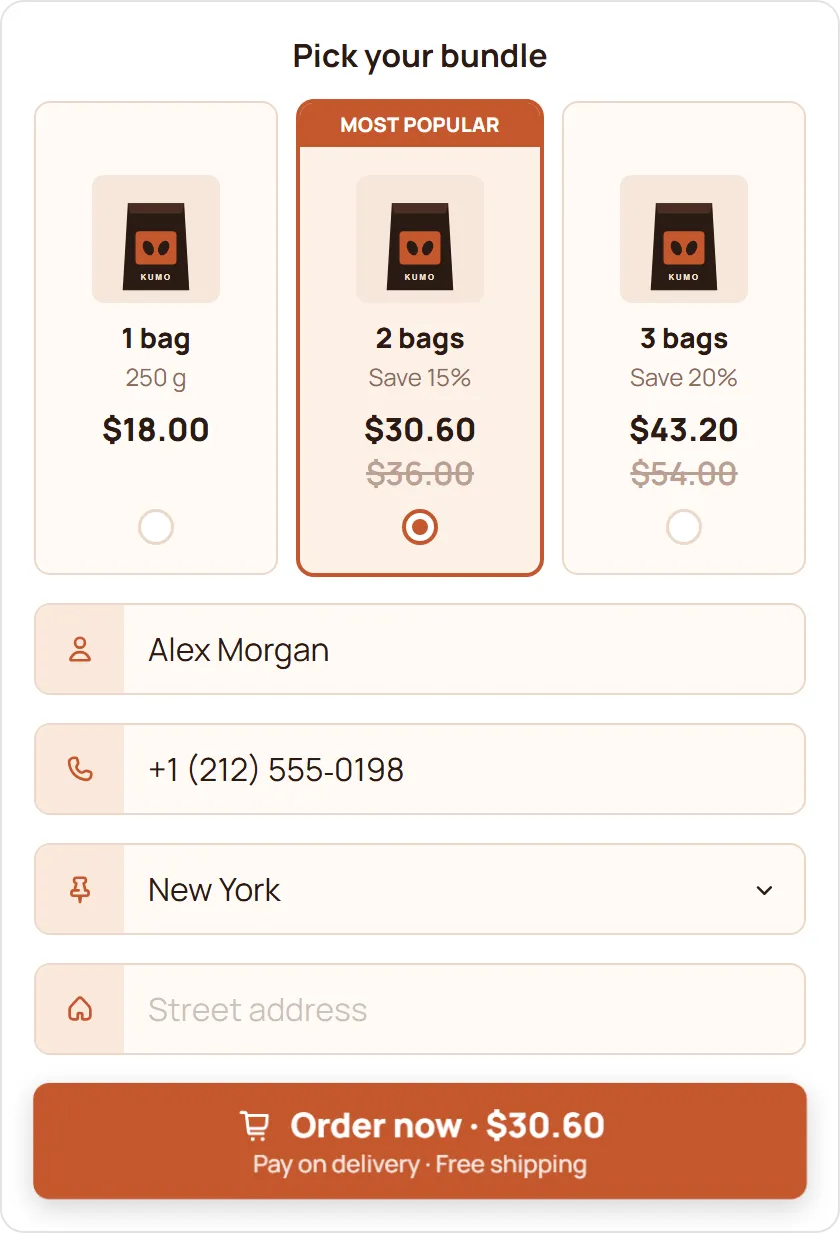
- EverCore COD Form: a cash-on-delivery order form on your storefront that creates orders in your store, with shipping rates, offers, upsells, spam protection, abandoned-order capture, Google Sheets export, ad-platform conversion tracking and order analytics.
- Order Tagger: tag new orders automatically using rules you define.
- Support: an in-app form for contacting us.
EverCore is a tool for merchants. We do not sell personal data, we are not a data broker, and we do not use your data or your buyers’ data for our own advertising.
Our role: controller and processor
For data about you and your staff (your account, billing and support conversations), we are the controller.
For data about your buyers that EverCore collects through the COD Form or reads from your orders, we act as a processor on your behalf. You are the controller of that data. You decide which features to turn on, which Google Sheet and ad platforms receive it, and you are responsible for your own privacy notice and consent banner on your storefront.
Shopify permissions we request, and why
When you install EverCore, you grant it the following Shopify access scopes. We use each one only for the purpose described.
Products
Read and write access to products. Used to read your catalogue, create products you import, set prices you edit on a page, and assign an EverCore template to a product.
Themes
Read and write access to themes. EverCore writes its own files into a theme you pick and checks which theme is live. Every file it adds is prefixed ec-; your own theme files are left in place, and shared settings and language files are merged rather than replaced.
Files
Write access to your store’s Files. Imported product images and AI-generated landing page images are uploaded to Shopify Files under your store, so they are hosted by Shopify.
Orders
Read and write access to orders. Used to create an order when a buyer submits the COD Form, and by Order Tagger to read new orders and apply tags.
Publications
Used to publish products EverCore creates to your Online Store sales channel.
Webhooks and app proxy
EverCore listens for Shopify’s mandatory privacy webhooks (customers/data_request, customers/redact, shop/redact), for app uninstall, for new orders (Order Tagger), and for billing and credit purchase events. Storefront requests from the COD Form reach EverCore through Shopify’s app proxy (/apps/evercore-cod/), which Shopify signs so we can verify they come from your store.
Data about you and your staff
- Store details: shop domain and ID, and the shop owner’s name, email and phone number as provided by Shopify.
- Access credentials: your Shopify access token, stored encrypted, and staff session details from Shopify (name and email) so you stay signed in.
- Google connection: if you connect Google Sheets, the email of the Google account you connect and the Google access and refresh tokens. EverCore requests the
drive.filescope, which only gives access to spreadsheets the app creates or that you pick, plusopenidandemailto show which account is connected. - Ad-platform tokens: access tokens you enter for Meta, TikTok, Snap or OpenAI Ads, stored encrypted.
- Your content: pages you generate, product details you import (including AliExpress links), and the audience, angle and tone choices you make.
- Customer research files: if you upload research files (TXT, PDF, MD, DOCX or CSV), we keep only the text extracted from them and a summary used to write your pages.
- Billing and usage: your plan, subscription status, credit balance, credit transactions and usage counts.
- Support messages: the name, email, topic and message you send through the support form.
We do not collect your payment card details. All billing is handled by Shopify.
Data about your buyers
All buyer data comes from the COD Form on your storefront and is processed on your behalf.
COD orders
When a buyer submits the COD Form we store: full name, phone number, email, province, city or commune, delivery type, shipping rate, cart items, totals, IP address, a browsing session ID, and the ID of the Shopify order created.
Abandoned orders
Once a buyer has typed a complete, valid phone number, the form saves what they have entered so far (such as name, phone, email, country, province, city, address, product, cart and offer), together with their IP address, browser user agent and signals the form measures to detect bots. If no order follows, this is written to your abandoned-orders Google Sheet after the delay you choose, so you can follow up.
Spam protection
When the form refuses an order because of your block lists or limits, we record the phone number, email or IP address involved and the reason.
Ad conversion events
When you connect an ad platform, we keep a delivery log of server-side events sent, containing hashed identifiers, IP address and user agent.
Form analytics
Form opens are recorded as a daily count per store, with no information about the visitor.
What we do not collect from buyers
We do not collect card or payment details (the form is cash on delivery) and we do not create Shopify customer accounts.
Order Tagger
Order Tagger stores order IDs, order names and the tags applied. It does not store buyer personal data.
How we use data
We use the data above only to:
- provide the features you use: generate pages, import products, create and tag orders, write rows to your Google Sheets and send conversion events to the ad platforms you connect;
- protect your store from spam and fake orders, using the rules you set;
- bill you through Shopify and keep track of plan limits and credits;
- check that EverCore page layouts on your storefront are covered by an active plan;
- answer your support requests; and
- keep EverCore secure, diagnose errors and improve reliability.
To be explicit: we do not sell, rent or trade personal data. We do not contact your buyers, build profiles or audiences from them, or use their data for our own marketing or for training AI models.
AI processing
EverCore uses OpenAI through its API to write page copy and generate images. Depending on the feature, we send OpenAI product titles and descriptions, text read from the AliExpress page you import, your research summary, your audience, angle and tone choices, and, for landing pages, up to three of your product photos (one of which is used as a reference for image generation).
We do not send buyer personal data to OpenAI for content generation. Under OpenAI’s API terms at the time of writing, data sent through the API is not used to train OpenAI’s models by default.
Generated images may depict people. These are synthetic images produced by the AI, not photographs of real individuals.
Sharing with third parties
Service providers we use
We share data with these providers only as needed to run EverCore:
- Shopify: the platform EverCore runs on, including billing, orders, products, themes and Files.
- OpenAI: writes page copy and generates landing page images, as described above.
- Railway: hosts the application and its database.
- Cloudflare R2: stores EverCore’s theme packages. It receives no merchant or buyer data.
- Error monitoring provider: receives technical error reports, which may include request details, so we can diagnose failures.
- Jina AI Reader: receives the public AliExpress link you paste, when needed to read the product page.
- AliExpress: receives requests for the public product page you import.
- Google: Google Sheets, Drive, OAuth and Picker, used to connect your Google account and write COD orders and abandoned orders to your own spreadsheets.
Ad platforms you connect
If you connect them, EverCore loads browser pixels on your storefront and sends server-side conversion events on your instruction to: Meta (Pixel and Conversions API), TikTok (Pixel and Events API), Snap (Pixel and Conversions API), Google (Google tag and Google Ads conversion) and OpenAI Ads (pixel and Conversions API).
Server-side events contain the buyer’s email, phone, first and last name, city, province, postal code, country and an external ID, all hashed with SHA-256 before sending. As the platforms require, the IP address, browser user agent and platform click IDs and cookies are sent unhashed.
Consent
The COD Form uses Shopify’s Customer Privacy API. Ad pixels load, and ad click IDs are stored, only after the buyer gives marketing consent. Server-side conversion events are not sent when the buyer refuses marketing consent. On themes that do not use Shopify’s consent tooling, consent is treated as given, so you are responsible for providing an appropriate consent banner where the law requires one.
Once rows are written to your Google Sheet or events are delivered to an ad platform, that data is held under your Google account or your ad account and governed by those providers’ terms. You are the controller of it.
Other disclosures
We may disclose data if required by law, to protect our rights or the security of EverCore, or as part of a merger or sale of our business, in which case this policy continues to apply to the data transferred.
Cookies and browser storage
This website
This website is a static informational site. It sets no advertising cookies and runs no third-party tracking or analytics scripts.
The EverCore app
Inside your Shopify admin, EverCore uses only strictly necessary cookies and session storage to keep you signed in.
Your storefront
The COD Form stores the following in your buyers’ browsers:
evcod_sid(session storage): a random ID so one browsing session counts as one abandoned order.evcod_*(local storage): ad click IDs from the landing link, such as Meta, TikTok, Snap or OpenAI Ads click references, kept for 7 days and only after marketing consent.evcod_test(local storage): a test-device token, only on devices you register for your team.
The form also reads existing ad cookies (such as Meta _fbp/_fbc, TikTok _ttp and the Snap cookie) to attach them to conversion events. Ad platforms’ own pixels set their own cookies once loaded, under their own policies.
Retention and deletion
Automatic retention periods
- Abandoned orders: 30 days after the last update.
- Blocked order attempts: 30 days.
- Ad conversion delivery logs: 30 days.
- Rows queued for Google Sheets: 7 days after they are written.
- Unused research files: 24 hours.
- COD orders: until a buyer’s data is erased through a
customers/redactrequest, or until the store’s data is deleted throughshop/redact. - Support messages: as long as needed to handle your request and keep a record of our support history. You can ask us to delete them at any time.
When you uninstall
On uninstall we clear your access token and the shop owner’s name, email and phone; delete staff sessions, Order Tagger history and research files; and cancel any active subscription. Shopify sends a shop/redact request 48 hours after uninstall, when we delete the rest of your store’s data as described below.
Generated pages, imported product data, and billing and credit records are kept so that your work and credit balance are restored if you reinstall, and to meet our accounting obligations. Email us to have your generated pages deleted.
Shopify privacy webhooks
customers/data_request: when a buyer asks you for their data, we provide you an export of their COD orders, unsubmitted form entries, queued sheet rows and tagged orders, matched by order ID, phone or email.customers/redact: we delete that buyer’s COD orders, abandoned orders, queued sheet rows, ad delivery logs, blocked attempts and Order Tagger records.shop/redact: we delete all COD Form data, settings (including ad-platform tokens), Google Sheet links and tokens, ad delivery logs, research files and summaries, sessions and the shop owner’s details. A minimal record of the store is kept, marked as deleted.
International transfers
EverCore and its service providers may process data in the United States and in other countries where those providers operate. Where data about buyers or merchants in other regions, such as the European Union, is transferred, we rely on our providers’ safeguards for international transfers.
Security
Data is transmitted over encrypted connections (HTTPS/TLS). Shopify access tokens and ad-platform tokens are stored encrypted, and credentials are never exposed to the storefront or to other merchants. Storefront requests are verified through Shopify’s signed app proxy. Access to production systems is limited to personnel who need it. No system is perfectly secure, but we take reasonable and appropriate measures to protect the data we hold.
Your rights
You can ask us at any time to tell you what data we hold about your store, to provide a copy, to correct it or to delete it. Email support@evercore.dev and we will respond within a reasonable time.
Buyers who want to access or delete their data should contact the merchant they ordered from. The merchant can make the request through Shopify, and we act on it as described above. If a buyer contacts us directly, we will refer them to the merchant.
Children
EverCore is a business tool for merchants and is not directed to children. We do not knowingly collect data about children.
Changes to this policy
If we change how EverCore handles data, we will update this page and change the “last updated” date at the top. Material changes will also be communicated to merchants with the app installed.